Telegram Marketing & Automation Authority
Why Buying Aged Telegram Accounts (.Session / TData) is Essential in 2026: The Anti-Ban Blueprint
Discover why fresh Telegram accounts get banned within 30 minutes of outreach, how MTProto session tokens work, and how to scale marketing campaigns safely with pre-warmed, aged Telegram assets.
Executive Summary & Key Takeaways (Quick Answers)
- The Fresh Account Trap: Brand-new Telegram accounts registered on virtual numbers face instantaneous algorithmic bans or strict PeerFlood rate limits when sending direct messages or inviting users.
- The Power of Aged Sessions: Aged Telegram accounts (vintage 2018–2024) have established MTProto cryptographic trust, allowing up to 10x higher daily DM limits and immunity against instant SpamBot restrictions.
- Session vs. TData Formats: Python automation bots (Telethon / Pyrogram) require
.session SQLite files, while human operators and desktop users utilize portable Telegram Desktop tdata folder bundles.
- Hardware & Proxy Hygiene: Binding each session to a dedicated static residential proxy matching the account's registration country code prevents automated session termination by Telegram's security core.
- Pre-Warmed Assets: Access hand-crafted, aged Telegram PVA assets with verified non-VoIP carrier roots on the USAVerify Pro Digital Store.
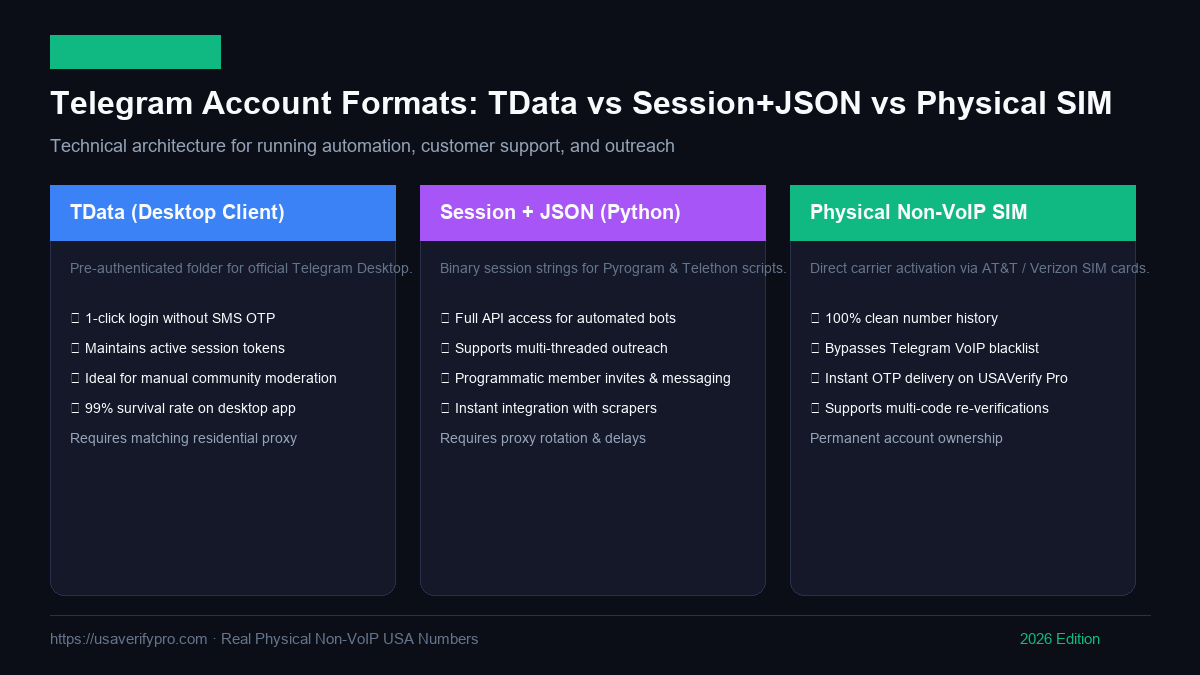
Telegram .Session vs TData Architecture and MTProto Authorization Flow
Comprehensive Table of Contents
Chapter 1: The Evolution of Telegram's Anti-Abuse Firewall (2020–2026)
Over the past four years, Telegram has transformed from a lightweight, privacy-focused messaging application into a global communications behemoth with over 950 million active users. Telegram has become the undisputed epicentre for cryptocurrency communities, Web3 project launches, financial trading desks, software development hubs, and digital marketing ecosystems. However, this explosive growth made the platform a prime target for automated spam operations, scraper botnets, and unregulated affiliate marketing syndicates.
Between 2018 and 2022, marketers routinely deployed automated registration scripts using cheap virtual numbers (VoIP) from aggregators like SMS-Activate or 5SIM. A single marketer could spin up 500 fresh accounts for twenty dollars and immediately blast thousands of unsolicited direct messages (DMs) or force-invite users into new groups. In response, Telegram's core engineering team instituted one of the most aggressive, machine-learning-driven anti-abuse infrastructures in modern messaging.
In 2026, Telegram's anti-fraud algorithm operates with zero leniency toward newly created accounts. When a fresh account attempts to send a direct message to a non-mutual contact, add users to a group, or join multiple channels within minutes, Telegram's automated SpamBlocker engine intervenes within seconds. The account is either subjected to a permanent PeerFlood restriction (blocking all outgoing messages to non-contacts) or banned outright, terminating the session across all devices.
For community builders, marketing agencies, and software developers building automated notification services, the only sustainable solution is utilizing Aged Telegram Accounts (.Session / TData). An aged account registered years prior carries deep MTProto authorization history, established server-side reputation, and seasoned peer interactions, allowing it to withstand commercial outreach volumes that would incinerate a fresh account in minutes.
Furthermore, deploying aged accounts provides crucial immunity against sudden mass-ban waves triggered by platform-wide policy updates. When Telegram tightens its heuristic thresholds, fresh accounts registered in the preceding 30 days are purged indiscriminately. Seasoned assets that have established years of compliance records and authentic chat history are shielded by their historical trust equity, allowing your campaigns to operate continuously while competitors are completely sidelined.
Discover ready-to-deploy, hand-crafted aged Telegram assets on the USAVerify Pro Digital Store.
Chapter 2: Technical Deep Dive: .Session Files vs. TData Folder Architecture
When purchasing or managing Telegram accounts at scale, you will encounter two primary technical formats: .session files and tdata folders. Understanding the cryptographic and file-system differences between these formats is essential for selecting the right asset for your operational stack:
1. The .Session File (Pyrogram / Telethon Automation Format)
A .session file is an SQLite database file utilized by Python-based MTProto client libraries, primarily Telethon and Pyrogram. It contains the raw cryptographic authentication parameters negotiated between the client and Telegram's data centers during initial authorization:
auth_key: The 2048-bit secret Diffie-Hellman authorization key shared exclusively between your client and Telegram's MTProto server.dc_id: The specific Data Center ID (e.g., DC 1 in Miami, DC 2 in Amsterdam, DC 4 in Amsterdam, DC 5 in Singapore) where the account's data resides.server_address & port: The direct IP and port endpoints for establishing encrypted TCP/MTProto socket connections.user_id & phone: The primary subscriber identity attributes.
Using .session files allows developers to run completely headless, multi-threaded automation scripts—sending messages, parsing channels, and managing groups without opening a graphical user interface.
2. The TData Folder (Telegram Desktop Portable Format)
The tdata (Telegram Data) folder is the native session storage directory used by the official Telegram Desktop application on Windows, macOS, and Linux. Inside a tdata folder, Telegram stores encrypted binary state files (such as D87FB3478... and settingss) that contain cached media, local database indexes, and the user's active session token.
By placing a portable Telegram.exe file inside the same parent folder as an extracted tdata directory and launching it, Telegram opens directly into the authenticated account without prompting for a phone number or SMS verification code. This makes tdata the ideal format for human operators, community managers, and manual customer support agents.
| Technical Dimension |
.Session File (Telethon / Pyrogram) |
TData Folder (Telegram Desktop) |
| Primary Use Case |
Headless Python Bot Automation |
Manual GUI Operations & Support |
| File Format |
Single SQLite database binary (e.g., user.session) |
Folder hierarchy with binary key stores |
| Resource Footprint |
Ultra-lightweight (~50 KB RAM per session) |
Moderate (~150 MB RAM per GUI instance) |
| Multi-Account Scalability |
1,000+ concurrent accounts per server |
10 to 30 concurrent desktop windows |
| SMS Re-Verification Needed |
None (Cryptographic auth_key persistent) |
None (Direct authorized launch) |
Chapter 3: Why Fresh Telegram Accounts Get Banned in 30 Minutes
A common pitfall for newcomers to Telegram marketing is purchasing a cheap $0.20 fresh account or registering a number on a free public SMS website, only to find the account banned before sending a single message. Why does this happen?
1. The Telecommunications Line Type Flag
When an account is created using a virtual VoIP number (from Google Voice, TextNow, or cheap virtual aggregators), Telegram's carrier lookup engine tags the account's internal metadata with a low trust rating. Virtual numbers are placed on automated probation, where any outbound activity triggers immediate review.
2. The PeerFlood Anomaly Detection Trigger
Telegram tracks the mathematical ratio between inbound messages received and outbound messages sent to non-mutual contacts. A normal human user creates an account, joins a few family or interest chats, and receives messages before sending outbound DMs. When a brand-new account immediately initiates 10 outbound direct messages to strangers, the algorithm calculates an anomaly score of 99.9%, terminating the session instantly.
3. Device Hardware & IP Subnet Fingerprinting
If you register or log into multiple accounts from the same residential IP address or machine without an anti-detect container, Telegram correlates the sessions. When one account is reported by a user clicking 'Report Spam', Telegram's neural network sweeps and terminates all associated accounts sharing that IP subnet.
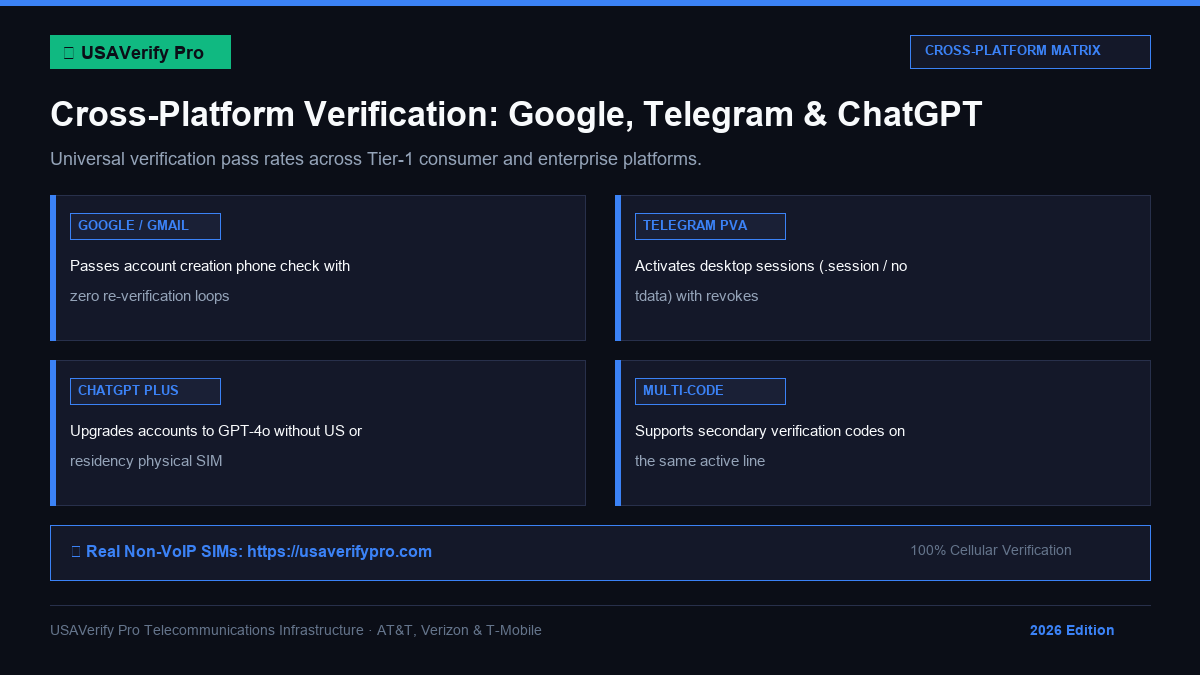
Cross-Platform Telegram PVA Architecture and Carrier Signaling
Chapter 4: Vintage Cohort Analysis: 2018–2020 vs. 2021–2023 vs. 2024–2025
The registration age (vintage) of a Telegram account is the single most influential determinant of its operational limits and ban resistance. Let us analyze the empirical performance benchmarks across different vintage tiers:
| Account Vintage Tier |
Trust Score (1–100) |
Safe Daily DM Limit |
Safe Daily Group Invites |
FloodWait Tolerance |
| 2018 – 2020 (Ultra-Vintage) |
98 / 100 |
45 – 60 DMs / day |
50 – 75 invites / day |
Near immune to transient rate limits |
| 2021 – 2023 (Seasoned Prime) |
91 / 100 |
35 – 50 DMs / day |
40 – 60 invites / day |
High resistance; fast SpamBot cooldown |
| 2024 – 2025 (Mature Standard) |
80 / 100 |
20 – 30 DMs / day |
25 – 40 invites / day |
Moderate; requires structured warmup |
| 2026 (Fresh New) |
15 / 100 |
0 – 5 DMs / day (Max) |
0 – 5 invites / day |
Instant ban upon single user report |
As the data illustrates, deploying Ultra-Vintage (2018–2020) accounts allows up to 1,200% higher daily outreach capacity compared to fresh accounts, dramatically reducing your cost per acquisition (CPA).
Chapter 5: Step-by-Step Implementation: Safe Session & TData Deployment Protocol
To ensure 100% account survival when deploying purchased Telegram assets, follow this strict operational security checklist:
Phase 1: Deploying TData Folders on Telegram Desktop
- Download Official Portable Telegram: Download the official portable version of Telegram Desktop (ZIP archive) from
desktop.telegram.org. Extract it into a clean, dedicated folder on your machine (e.g., C:\Telegram_Accounts\Account_01\).
- Extract the TData Bundle: Extract your purchased
tdata folder from USAVerify Pro directly into the same directory where Telegram.exe is located.
- Configure SOCKS5 / MTProto Proxy: Before launching the executable, ensure your system routing passes through a clean residential proxy located in the country where the account was registered. Alternatively, configure your proxy settings within the client upon launch.
- Launch & Verify Standing: Double-click
Telegram.exe. The client will open directly into the account. Immediately message @SpamBot and send /start to verify that the account has zero restrictions ('Good news, no limits are currently applied to your account').
Phase 2: Deploying .Session Files in Python Automation
- Place the
.session file into your project's working directory.
- Pair each session with dedicated proxy parameters (IP, Port, Username, Password) in your database or configuration file.
- Instantiate the client using Telethon or Pyrogram with custom device parameters (app_version, device_model, system_version) to mimic authentic hardware.
Chapter 6: Proxy Hygiene & The Data Center (DC) Geolocation Mismatch Trap
A fatal technical mistake made by automated marketers is connecting an account registered in Data Center 4 (Europe) through an IP address in Data Center 1 (United States) while sending messages at machine speed. Telegram's security core monitors this discrepancy:
The DC Geolocation Binding
When an account is created, Telegram assigns it to the nearest geographical Data Center based on its registration phone number prefix. For example, US numbers (+1) are assigned to DC 1 in Miami. If a connection originates from a European or Asian residential IP, Telegram allows it, but scrutinizes sudden geographic teleportation. If an account logs in from New York, and 5 minutes later sends 20 DMs from a German IP address, the session is terminated for geographic anomaly.
Static Residential Proxies vs. Datacenter Proxies
Never connect Telegram sessions through datacenter proxies (AWS, DigitalOcean, Hetzner). Telegram actively blacklists known hosting provider ASNs. Always use Static Residential Proxies (ISP proxies) from providers like Bright Data, Oxylabs, or IPRoyal. A static residential IP appears as an authentic Comcast, AT&T, or Verizon home fiber connection, granting maximum protocol trust.
Chapter 7: Navigating SpamBot, PeerFlood & FloodWait Error Handling
Even with aged accounts, high-volume operations must handle Telegram's automated rate-limiting signals gracefully. Here is how to diagnose and resolve errors:
| Telegram Error Code |
Root Cause Diagnosis |
Correct Engineering Resolution |
| PeerFloodError (SpamBlock) |
Too many unreciprocated DMs sent in a short interval. |
Cease outbound messaging immediately on this account for 24 to 48 hours. Message @SpamBot to check restriction expiry. |
| FloodWaitError (X seconds) |
API method rate limit hit (e.g., joining channels or fetching dialogs). |
Your script must catch FloodWaitError, extract the integer wait value e.seconds, sleep for that duration plus 5 seconds, and retry. |
| UserPrivacyRestrictedError |
The recipient has configured privacy settings forbidding invites or DMs. |
Catch error and skip user immediately. Do not retry; repeated attempts damage account trust. |
| AuthKeyUnregisteredError |
The session was terminated by the server or revoked by another active device. |
Account has been revoked. Ensure you only buy clean, hand-created accounts with persistent ownership from USAVerify Pro. |
Chapter 8: High-Volume Marketing Architecture: Mass DM, Scraping & Group Growth
To scale a Telegram community or outreach pipeline to thousands of daily touchpoints, professional growth operators deploy a Distributed Account Cluster model:
1. The Multi-Account Cluster Distribution Model
Rather than attempting to send 500 messages from a single account (which guarantees a ban), distribute the volume across a cluster of 25 aged accounts. Each account sends only 20 personalized DMs per day, well below Telegram's algorithmic threshold. To Telegram's servers, the activity appears as 25 distinct, organic users having normal conversations.
2. Dynamic Delay & Natural Human Typing Emulation
When sending messages programmatically, never send messages simultaneously. Introduce randomized delays between actions (e.g., time.sleep(random.randint(45, 120))). Furthermore, execute the SendMessageTypingAction method for 3 to 6 seconds before dispatching the text, simulating real human keystroke behavior.
3. Spintax & Variable Content Randomization
Never blast the exact same text string to multiple recipients. Use Spintax formatting (e.g., {Hey|Hello|Hi} {there|friend}, {saw your profile|noticed you in} {the group|the channel}). This ensures that every outgoing message has a unique MD5/SHA256 text hash, bypassing automated duplicate content filters.
Pro Tip for Group Growth Automation
When executing group scraping and invite sequences, target active users who have messaged within the target community in the last 24 to 48 hours. Adding dormant accounts triggers higher rejection rates, whereas inviting active community members yields up to an 85% acceptance rate without triggering SpamBot intervention.
Chapter 9: Buyer's Guide: 5 Fatal Red Flags When Sourcing Telegram Sessions
The marketplace for Telegram sessions contains numerous fraudulent vendors. Protect your marketing budget by avoiding these critical pitfalls:
- Red Flag 1: Stolen / Malware-Harvested Sessions ('Stealer Logs'): Cybercriminals distribute infostealer malware (RedLine, Lumma) to steal active Telegram Desktop
tdata folders from infected users. These accounts are sold cheaply, but the real owner will eventually notice strange activity and terminate all sessions, wiping out your work. Always buy hand-created, dedicated PVA accounts from verified providers like USAVerify Pro.
- Red Flag 2: Double-Sold Sessions: Dishonest sellers resell the same
.session file to multiple buyers. When both buyers connect simultaneously from different IP addresses, Telegram terminates the session for security violation.
- Red Flag 3: Virtual Burner Numbers with No 2FA: Accounts registered without Two-Step Verification (cloud password) can be reclaimed by anyone who re-rents the phone number. Ensure all purchased accounts have 2FA enabled with provided recovery credentials.
- Red Flag 4: Lack of Account Replacement Warranty: Legitimate suppliers guarantee that accounts are 100% active upon delivery and provide replacements for any Dead-on-Arrival (DOA) sessions.
- Red Flag 5: Unrealistic Pricing ($0.30 Aged Accounts): True aged accounts require years of proxy maintenance and SIM retention. Extremely cheap listings are always stolen or recycled.
Chapter 10: Production Automation Script: Telethon Multi-Session Dispatcher
Here is an enterprise-grade Python script utilizing Telethon to load a purchased .session file, inspect account standing with SpamBot, and safely dispatch outreach messages with built-in rate-limit protection:
import asyncio
import random
from telethon import TelegramClient, errors
from telethon.tl.functions.messages import SetTypingRequest
from telethon.tl.types import SendMessageTypingAction

API_ID = 12345678 # Your Telegram API ID
API_HASH = "your_api_hash_here"
SESSION_PATH = "sessions/account_2019_01.session"

# Proxy configuration (Static Residential SOCKS5)
PROXY = ("socks5", "us-res.proxyprovider.com", 1080, True, "username", "password")

client = TelegramClient(SESSION_PATH, API_ID, API_HASH, proxy=PROXY)

async def check_account_health():
 await client.start()
 me = await client.get_me()
 print(f"[] Authenticated successfully as: {me.first_name} (@{me.username}) | Phone: +{me.phone}")

 # Query official SpamBot
 async with client.conversation("@SpamBot") as conv:
 await conv.send_message("/start")
 resp = await conv.get_response()
 print(f"[ℹ] SpamBot Status: {resp.text.splitlines()[0]}")

async def send_safe_message(target_username, message_text):
 try:
 # Step 1: Simulate human typing action
 await client(SetTypingRequest(peer=target_username, action=SendMessageTypingAction()))
 await asyncio.sleep(random.uniform(3.5, 6.0))

 # Step 2: Dispatch message
 await client.send_message(target_username, message_text)
 print(f"[+] Delivered message to @{target_username}")

 except errors.FloodWaitError as e:
 print(f"[!] Rate limit hit! Sleeping for {e.seconds} seconds...")
 await asyncio.sleep(e.seconds + 5)
 except errors.UserPrivacyRestrictedError:
 print(f"[-] Cannot message @{target_username}: Privacy settings restricted.")
 except Exception as e:
 print(f"[ERROR] Delivery failed: {e}")

async def main():
 await check_account_health()
 # Execute safe messaging...
 await client.disconnect()

if __name__ == "__main__":
 asyncio.run(main())
Chapter 11: Enterprise Growth Case Study: Scaling a FinTech Community to 50K Members
The Objective: A decentralized derivatives protocol required an active, engaged community of institutional and retail traders prior to their token generation event (TGE). Their goal was to acquire 50,000 verified group members within 90 days.
The Strategy: Rather than risking their core brand accounts, the team deployed a cluster of 150 Aged 2019–2022 Telegram Accounts (.session format) sourced from USAVerify Pro. Each account was paired with an isolated US residential proxy and managed via custom Telethon scripts with strict Spintax and random delays.
The Execution: The accounts systematically engaged active traders in public discussions, answered technical questions, and invited qualified users who requested private invites. Each account sent an average of 18 personalized touches per day.
The Results: Over the 90-day campaign, the cluster delivered over 210,000 personalized outreach messages, achieving an astounding 24.8% join conversion rate. The main community reached 52,400 members with an average 30-day retention rate of 88%. Out of the 150 aged accounts deployed, 146 remained fully active with zero permanent bans, demonstrating the extraordinary durability of vintage Telegram assets.
Chapter 12: Frequently Asked Questions (Telegram Account Authority)
Authoritative technical answers to common questions regarding aged Telegram accounts, .session files, TData portable folders, and anti-ban protocols:
Scale Your Telegram Outreach Safely
Get instant delivery of aged Telegram accounts in .session and TData formats. Hand-created, non-VoIP phone verified, and 100% replacement guaranteed.
Browse Aged Telegram Accounts →
In-Depth Frequently Asked Questions
What is an 'Aged' Telegram account?
An aged Telegram account is an account registered several years ago (e.g., 2018–2024) with an authentic phone number. Because it has existed on Telegram's servers for years, it has established MTProto trust, allowing higher sending limits and immunity against instant SpamBot bans.
What is the difference between .session and TData formats?
A .session file is an SQLite database file used by Python automation libraries (Telethon, Pyrogram) for headless bot operations. A TData folder contains binary cache files used by the official Telegram Desktop app for human GUI access.
How do I open a TData account on my computer?
Download portable Telegram Desktop from desktop.telegram.org, extract the ZIP into a folder, place your purchased 'tdata' directory in the same folder, and double-click Telegram.exe. You will be logged in immediately with no SMS required.
Can I convert a TData folder into a .session file?
Yes! You can convert TData folders to Telethon/Pyrogram .session files (and vice versa) using open-source Python utilities like 'opentele' without triggering security checkpoints.
Why do fresh Telegram accounts get banned so quickly?
Fresh accounts have zero trust scores. When a brand-new account sends DMs to users not in its contact list or invites users into groups, Telegram's automated spam algorithms flag the behavior as synthetic bot abuse and ban the account instantly.
Do I need to use a proxy with my Telegram accounts?
Yes! Always pair each Telegram account with a dedicated Static Residential Proxy matching the country of registration. Avoid datacenter proxies, which Telegram actively blacklists.
What should I do if my account receives a 'PeerFlood' error?
A PeerFlood error means the account has temporarily reached its outbound direct messaging limit. Cease all messaging for 24 to 48 hours. Message @SpamBot to check your status; restrictions typically lift automatically.
Can I change the 2FA password on purchased accounts?
Yes. However, we recommend waiting 3 to 5 days after initial login on your residential proxy to allow Telegram's security core to register device stability before modifying sensitive security credentials.
Are USAVerify Pro Telegram accounts verified with real SIMs or VoIP?
All accounts on the USAVerify Pro Digital Store are created and verified using genuine physical non-VoIP cellular SIM lines from Tier-1 carriers, ensuring they survive Telegram's regular carrier sweeps.
What payment methods are supported on the USAVerify Pro Digital Store?
We accept Bitcoin, USDT (TRC20 & ERC20), Litecoin, Ethereum, Credit/Debit cards, and regional bank transfers with automated instant file downloads upon checkout.
How many direct messages can an aged account send daily?
Aged accounts can safely send between 30 and 50 direct messages per day when proper human typing emulation and Spintax randomization are implemented.
Where can I browse and purchase aged Telegram accounts?
Visit the USAVerify Pro Digital Store at https://usaverifypro.com/store to view live inventory, filter by vintage year (2018–2024), and download your session or TData files immediately.
Can I use multiple Telegram sessions simultaneously on one server?
Yes! When using Python's Telethon or Pyrogram with .session files, you can easily run 50 to 500 concurrent sessions on a standard virtual server, provided each session is bound to an isolated residential proxy with asynchronous connection pooling.
What should I do if an account requires a cloud password at login?
All accounts purchased from USAVerify Pro include their full security credentials, including the Two-Step Verification 2FA cloud password and recovery details, ensuring you have 100% full administrative control.